Privoxy: The Essential Privacy Proxy for 2026
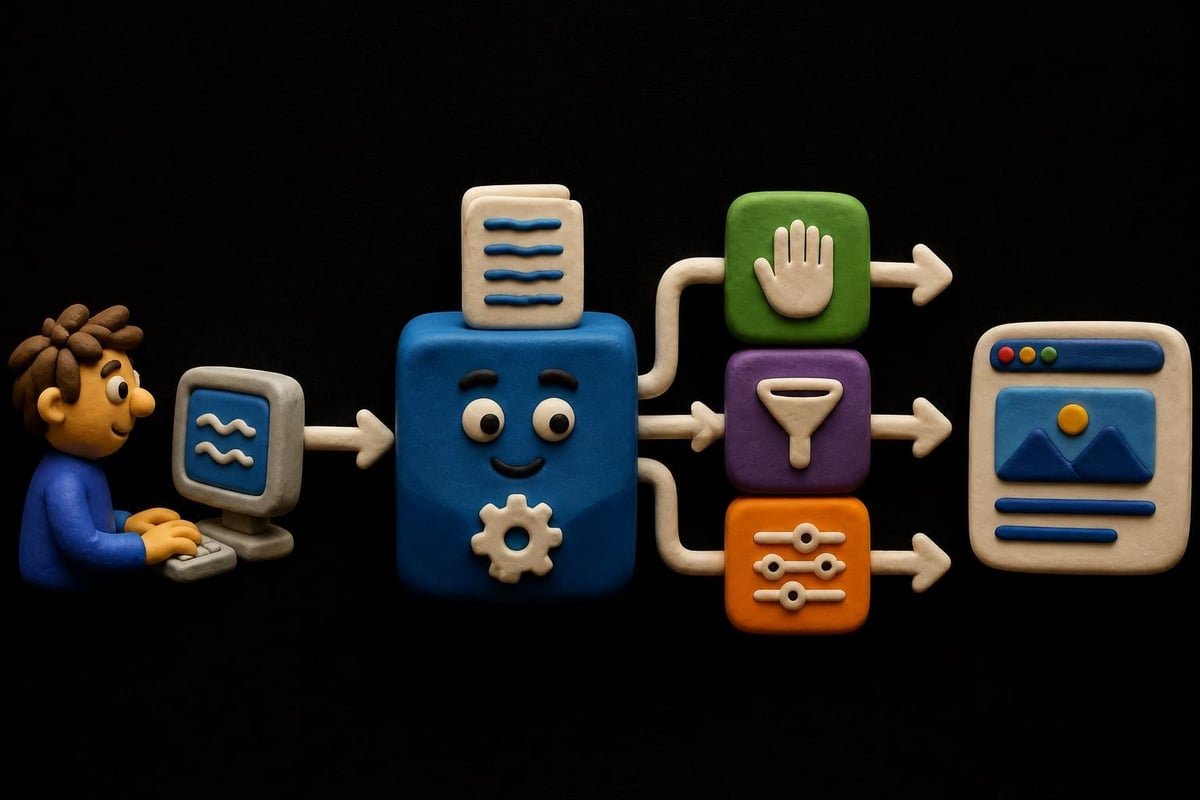
Privacy concerns continue to dominate online conversations in 2026, with users seeking greater control over their digital footprints. Privoxy stands as a non-caching web proxy with advanced filtering capabilities, designed to enhance privacy, remove unwanted content, and modify web page data before it reaches your browser. Unlike commercial proxy services, privoxy operates locally on your machine or network, giving you complete control over how HTTP and HTTPS traffic gets filtered and modified. This open-source tool has evolved significantly since its inception, offering powerful features for users who demand granular control over their browsing experience without relying solely on third-party services.
What Makes Privoxy Different from Traditional Proxies
Traditional proxy services route your traffic through remote servers, masking your IP address and providing access to geo-restricted content. Privoxy takes a fundamentally different approach by focusing on content filtering and privacy enhancement rather than IP masking.
Key capabilities that set privoxy apart:
- Advanced ad and banner blocking through pattern matching
- Cookie management and selective deletion
- HTTP header modification for enhanced anonymity
- Content filtering using regular expressions
- Pop-up window elimination
- JavaScript filtering and modification
The official Privoxy user manual details how these features work together to create a comprehensive privacy layer. What makes this particularly valuable is the complete transparency of the filtering process, since all rules and configurations are stored locally in plain text files you can inspect and modify.
Installation and Basic Setup
Getting privoxy running on your system requires minimal effort across major platforms. Most Linux distributions include privoxy in their standard repositories, making installation straightforward through package managers.
For Debian-based systems, the Debian package for privoxy provides a well-maintained version with systemd integration. Installation follows the standard pattern:
- Update package lists and install privoxy
- Configure the main configuration file at
/etc/privoxy/config - Set up actions files to define filtering behavior
- Start the privoxy service and enable it at boot
- Configure your browser to use localhost:8118 as the HTTP proxy
The default configuration provides reasonable privacy protection out of the box, but the real power emerges when you customize actions files. These files determine which sites get filtered, what content gets blocked, and how headers get modified based on URL patterns.
Configuration Architecture and Actions Files
Understanding privoxy's configuration architecture is essential for leveraging its full potential. The system uses three main types of files that work together to control behavior.
| File Type | Purpose | Example Use Case |
|---|---|---|
| config | Main settings, listen address, log levels | Set listening port to 8118, enable forwarding |
| Actions files | URL-pattern based rules for filtering | Block ads on news sites, allow cookies for banking |
| Filter files | Content modification patterns | Remove specific HTML elements, modify JavaScript |
The detailed configuration reference explains how these files interact. Actions files use a hierarchical system where more specific patterns override general ones, giving you precise control over how different sites get treated.
Common action categories include:
- block - completely prevent requests to matched URLs
- filter - apply content transformations
- crunch-incoming-cookies - reject cookies from servers
- crunch-outgoing-cookies - prevent sending cookies to servers
- hide-user-agent - modify or remove user agent strings
- add-header - insert custom HTTP headers
Advanced Privacy Features and Header Management
HTTP headers reveal substantial information about your browser, operating system, and browsing habits. Privoxy excels at header manipulation, allowing you to present a controlled digital fingerprint to websites.
The user agent string alone can identify your browser version, operating system, device type, and installed plugins. Privoxy can replace this with a generic string or rotate between several predefined options. Referrer headers, which tell websites where you came from, can be selectively stripped or modified based on domain patterns.
Security Considerations and Best Practices
While privoxy provides powerful privacy features, understanding its security model is crucial. The tool operates as a local HTTP proxy, which means all traffic passes through it unencrypted unless you're accessing HTTPS sites. This makes privoxy an excellent complement to, but not a replacement for, encrypted connections and VPN services.
According to research on proxy service security, understanding the trust model of any proxy system is essential. Since privoxy runs locally, you eliminate the risk of a third-party proxy logging or modifying your traffic, but you also need to secure the configuration files and ensure the service itself isn't exposed to the network.
Security hardening checklist:
- Bind privoxy to localhost only unless specifically needed on LAN
- Use strong file permissions on configuration directories
- Regularly update to the latest stable version
- Audit actions files for unintended rule interactions
- Implement forwarding to authenticated upstream proxies when needed
- Monitor log files for unusual patterns or errors
The OWASP Developer Guide offers additional insights on secure proxy deployment and HTTP header privacy considerations that complement privoxy's capabilities.
Integrating Privoxy with Other Privacy Tools
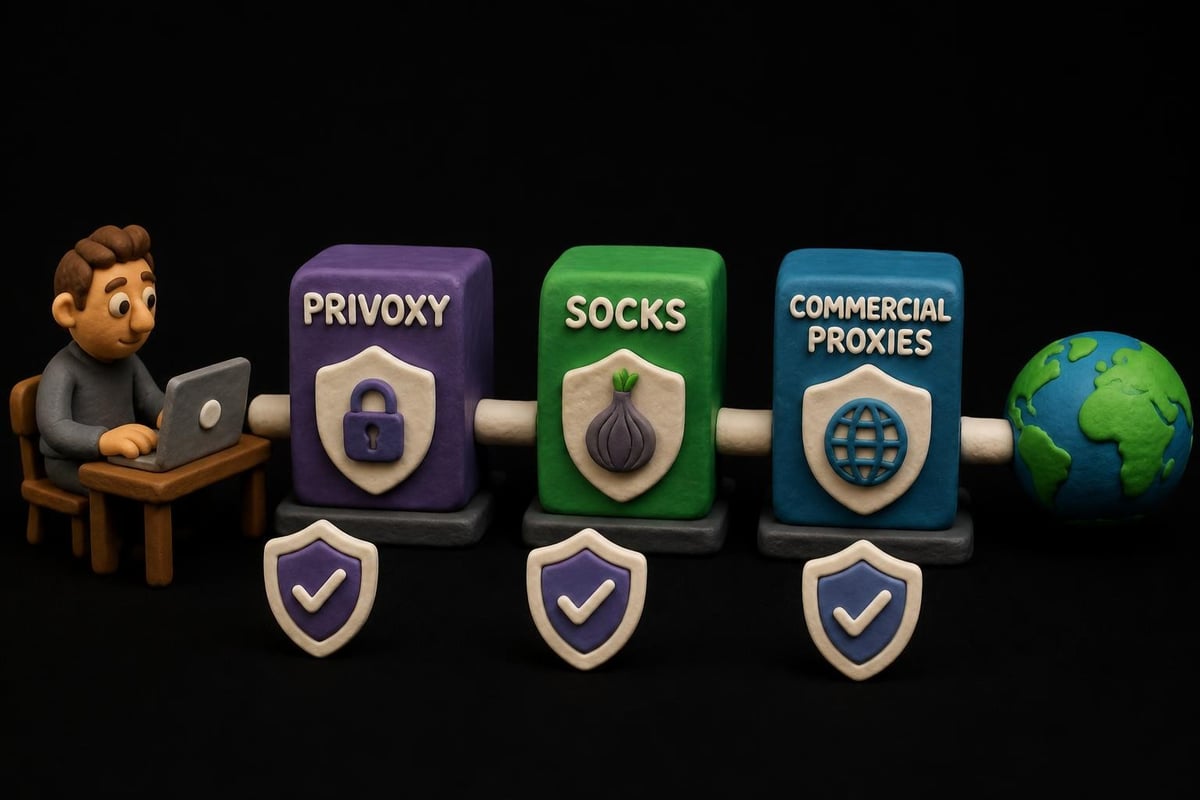
Privoxy's real power emerges when combined with other privacy technologies. The most common integration involves using privoxy as a filtering layer in front of Tor, providing both anonymity and content filtering.
Privoxy and Tor: A Privacy Powerhouse
The Tor network provides anonymous routing by bouncing your traffic through multiple relays, making it extremely difficult to trace. However, Tor doesn't filter content or manage cookies. This is where privoxy becomes invaluable.
By configuring privoxy to forward to a local Tor SOCKS proxy, you get the best of both worlds:
- Content filtering and ad blocking from privoxy
- Anonymous routing and IP masking from Tor
- Cookie and header management before traffic enters Tor
- JavaScript filtering to reduce fingerprinting
The dockage/tor-privoxy Docker container demonstrates a production-ready configuration combining both tools. This containerized approach simplifies deployment and ensures consistent behavior across environments.
Commercial Proxy Integration
For use cases requiring specific geographic locations or high-speed connections, privoxy can forward to commercial proxy services while still providing local filtering. This hybrid approach combines the speed and location benefits of services like PinguProxy's datacenter proxies with privoxy's content filtering.
The forwarding configuration accepts both HTTP and SOCKS proxies, supporting authentication when required. This flexibility allows you to:
- Use privoxy for ad blocking and privacy filtering
- Forward to rotating residential proxies for scraping
- Chain multiple proxies for enhanced anonymity
- Apply different forwarding rules based on URL patterns
Modern Deployment: Systemd and Containerization
Running privoxy as a system service ensures it starts automatically and integrates properly with modern Linux distributions. The Fedora package includes systemd unit files that handle service lifecycle management.
Systemd integration benefits:
- Automatic restart on failure
- Dependency management for network availability
- Proper privilege dropping after startup
- Journal integration for centralized logging
- Resource limits to prevent runaway processes
The Debian manpage for privoxy documents command-line options and service behavior, essential for troubleshooting and custom deployments.
For containerized environments, Docker images provide isolation and reproducibility. A minimal Dockerfile for privoxy includes the base package, custom configuration files, and appropriate user permissions. Volume mounts allow configuration updates without rebuilding containers.
Real-World Use Cases and Performance Tuning
Understanding how privoxy performs in different scenarios helps optimize configuration for specific needs. The tool handles varying workloads differently based on filter complexity and traffic volume.
| Use Case | Configuration Focus | Performance Impact |
|---|---|---|
| Ad blocking | Extensive URL patterns | Low (mostly regex matching) |
| Content rewriting | Complex filter files | Medium (content parsing overhead) |
| Header privacy | Action-based modifications | Minimal (header manipulation) |
| Corporate filtering | Large pattern lists | Medium (pattern matching at scale) |
Web Scraping and Development
Developers frequently use privoxy during web scraping projects to normalize requests and remove tracking elements. By filtering out unnecessary JavaScript and modifying headers, scraping scripts become more efficient and less detectable.
The tool also serves as a debugging proxy, allowing inspection and modification of HTTP traffic without specialized tools. Enabling debug logging reveals exactly how privoxy processes each request, useful for troubleshooting complex filtering rules.
Content Research and Testing
Privacy researchers and security professionals use privoxy to analyze how websites track users and serve different content based on headers. By systematically modifying user agents, referrers, and other identifying information, researchers can map tracking behavior and test website responses.
This same capability benefits businesses testing how their services appear to users with different browser configurations or privacy settings. Privoxy provides a controlled environment for A/B testing privacy-conscious configurations.
Filter Development and Custom Rules
Creating effective filters requires understanding both HTTP/HTML structure and regular expression syntax. Privoxy's filter files use Perl-compatible regular expressions, offering powerful pattern matching capabilities.
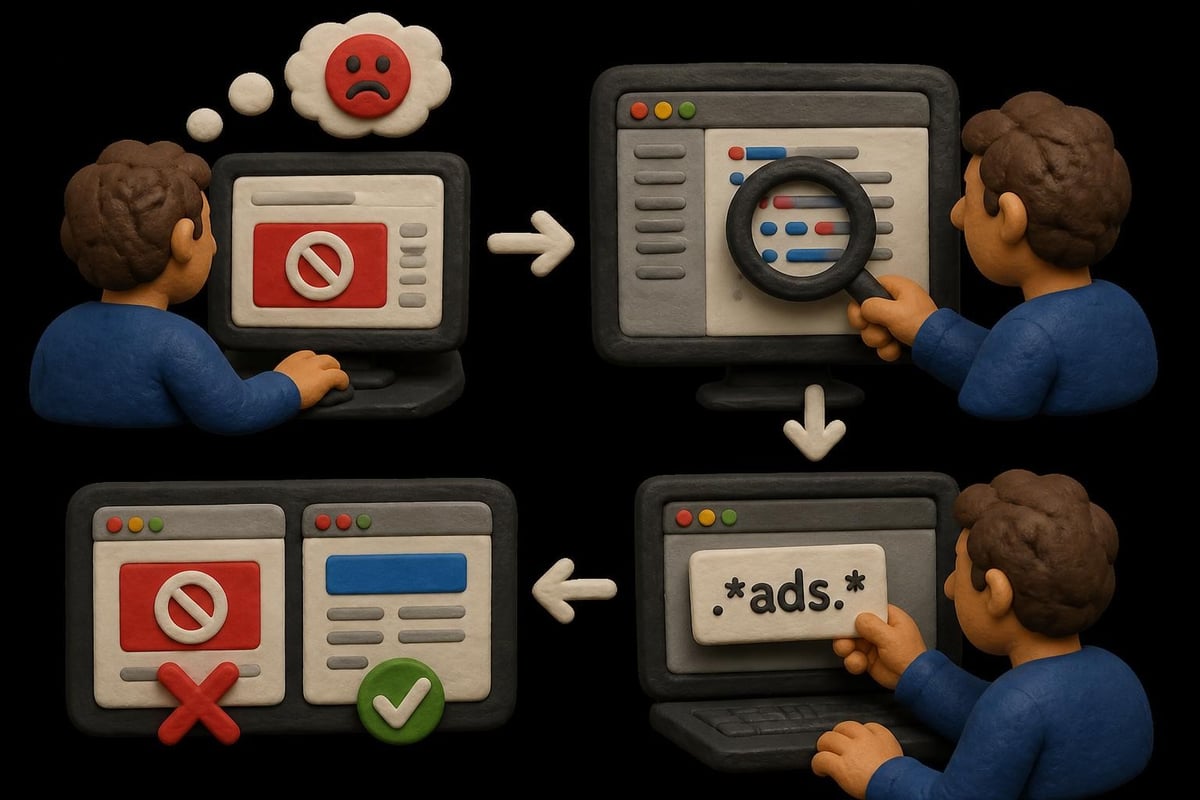
Filter development workflow:
- Identify unwanted content through browser inspection
- Write regex pattern to match the content
- Test pattern in isolation using regex tools
- Add filter to appropriate actions file section
- Reload configuration and verify behavior
- Monitor logs for unintended matches
The Wikipedia article on Privoxy provides historical context on how filtering evolved from earlier projects, offering perspective on why certain design decisions were made. Understanding this heritage helps grasp privoxy's philosophy and configuration logic.
Pattern Matching Best Practices
Efficient pattern matching significantly impacts performance. Overly broad patterns create false positives, blocking legitimate content. Too narrow patterns miss variations of unwanted content.
Optimization strategies include:
- Anchor patterns to specific HTML structures when possible
- Use non-capturing groups to reduce memory overhead
- Test patterns against saved page samples before deployment
- Comment extensively to document pattern intent
- Group related patterns in dedicated filter files
Network-Wide Privacy with Privoxy
Deploying privoxy as a network-wide transparent proxy extends privacy protection to all devices on a LAN. This approach particularly benefits IoT devices, smart TVs, and other equipment with limited configuration options.
Setting up transparent proxying requires configuring your network router or gateway to redirect HTTP traffic through the privoxy instance. While HTTPS traffic can't be transparently proxied without certificate manipulation, many devices still generate substantial HTTP traffic for telemetry and ads.
The configuration changes slightly for network-wide deployment:
- Bind privoxy to a LAN-accessible address instead of localhost
- Implement access controls to prevent abuse
- Scale buffer sizes for concurrent connections
- Consider hardware requirements for throughput needs
- Monitor resource usage under typical load
Business networks often deploy privoxy on dedicated hardware or VMs to handle enterprise-scale filtering. Combined with logging to a centralized system, administrators gain visibility into privacy protection effectiveness.
Maintenance and Troubleshooting
Keeping privoxy running smoothly requires periodic maintenance and occasional troubleshooting. Log files provide the first line of insight when issues arise.
Common issues and solutions:
| Problem | Cause | Resolution |
|---|---|---|
| Websites not loading | Overly aggressive blocking | Temporarily disable filters, identify specific rule |
| Slow performance | Complex regex in filters | Optimize patterns, reduce filter scope |
| Configuration ignored | Syntax errors in files | Check logs for parsing errors, validate syntax |
| Forwarding failures | Upstream proxy unavailable | Verify upstream connectivity, check credentials |
Debug logging levels range from minimal to verbose, with higher levels providing detailed request processing information. For performance-sensitive deployments, keep debug levels low in production while enabling verbose logging during troubleshooting sessions.
Regular updates ensure access to the latest features and security fixes. The privoxy development team continues active maintenance, addressing bugs and adapting to evolving web technologies. Subscribing to release announcements helps track when updates become available.
Advanced Scenarios and Edge Cases
Power users push privoxy beyond basic filtering into sophisticated traffic manipulation scenarios. These advanced configurations demonstrate the tool's flexibility.
Sophisticated use cases:
- Dynamic filter switching based on time of day or network location
- Integration with DNS-based blocking for multi-layer protection
- Content injection for accessibility modifications
- Protocol-specific handling for WebSocket connections
- Conditional forwarding based on content type or file size
Some users run multiple privoxy instances with different configurations, selecting which instance to use based on the task at hand. A development instance might log everything verbosely, while a production instance prioritizes performance and minimal logging.
Load balancing across multiple upstream proxies requires external tools, but privoxy can rotate between several forwarding targets using time-based or random selection. This provides basic redundancy when working with commercial proxy pools.
Privoxy remains a powerful tool for users who demand complete control over their web privacy and content filtering in 2026. Whether you're blocking ads, researching tracking mechanisms, or integrating with anonymous networks, privoxy's flexible configuration and transparent operation provide capabilities unmatched by black-box solutions. For users requiring both advanced filtering and high-speed proxy access across multiple locations, combining privoxy with a service like PinguProxy delivers comprehensive privacy protection. PinguProxy's zero-log datacenter and residential proxies complement privoxy's local filtering, creating a defense-in-depth approach to online privacy that addresses both content filtering and IP-level anonymity with 10Gbps bandwidth and 24/7 support.